ENTERPRISE UNIFIED
SINGLE SIGN-ON
Centralized identity and access platform enabling secure cross-domain authentication, role provisioning, JWT lifecycle management, and TOTP multi-factor security.
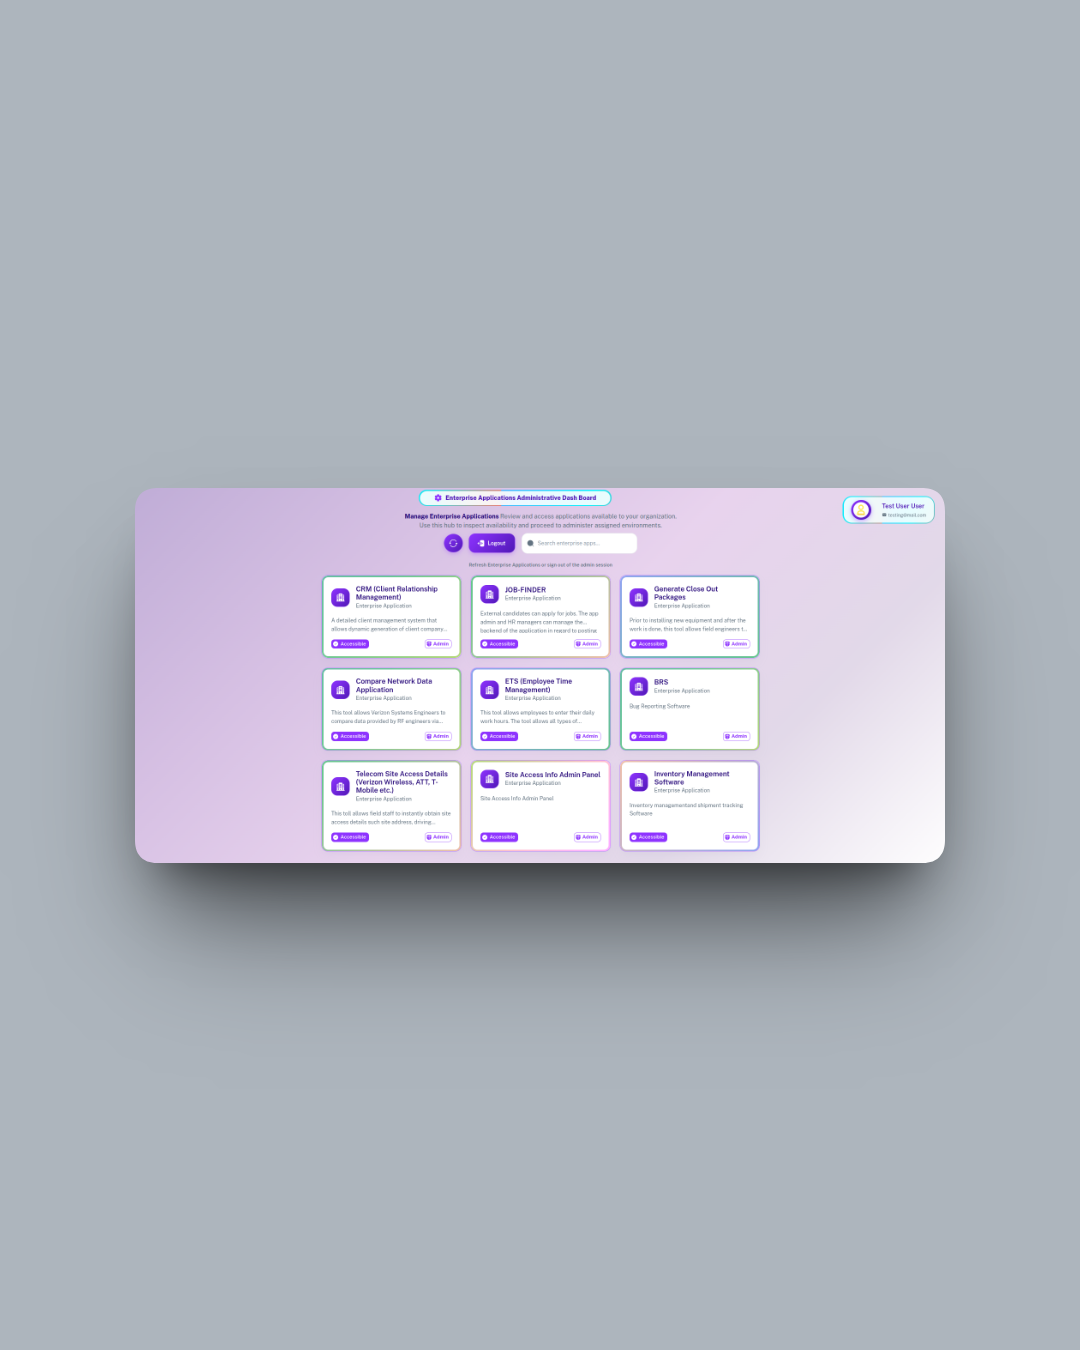
Operational Friction
Managing user identities and credentials across disparate internal and partner applications created severe administrative overhead, delayed employee onboarding, and introduced critical security blind spots.
Engineered Solution
Architected a centralized OAuth 2.0 and JWT identity hub fortified with Google TOTP 2FA, automated domain request workflows, and cross-application session synchronization.
Architecture & Backend Implementation
Security Architect & Full-Stack Lead: Designed cryptographic token lifecycles, zero-trust access control, and real-time monitoring governance.
Designed asymmetric RS256 JWT lifecycle, token rotation, and instant Redis blacklisting.
Implemented Google Authenticator TOTP with encrypted secret storage and rate-limited recovery.
Built queue-based Excel infrastructure processing engine with automated validation.
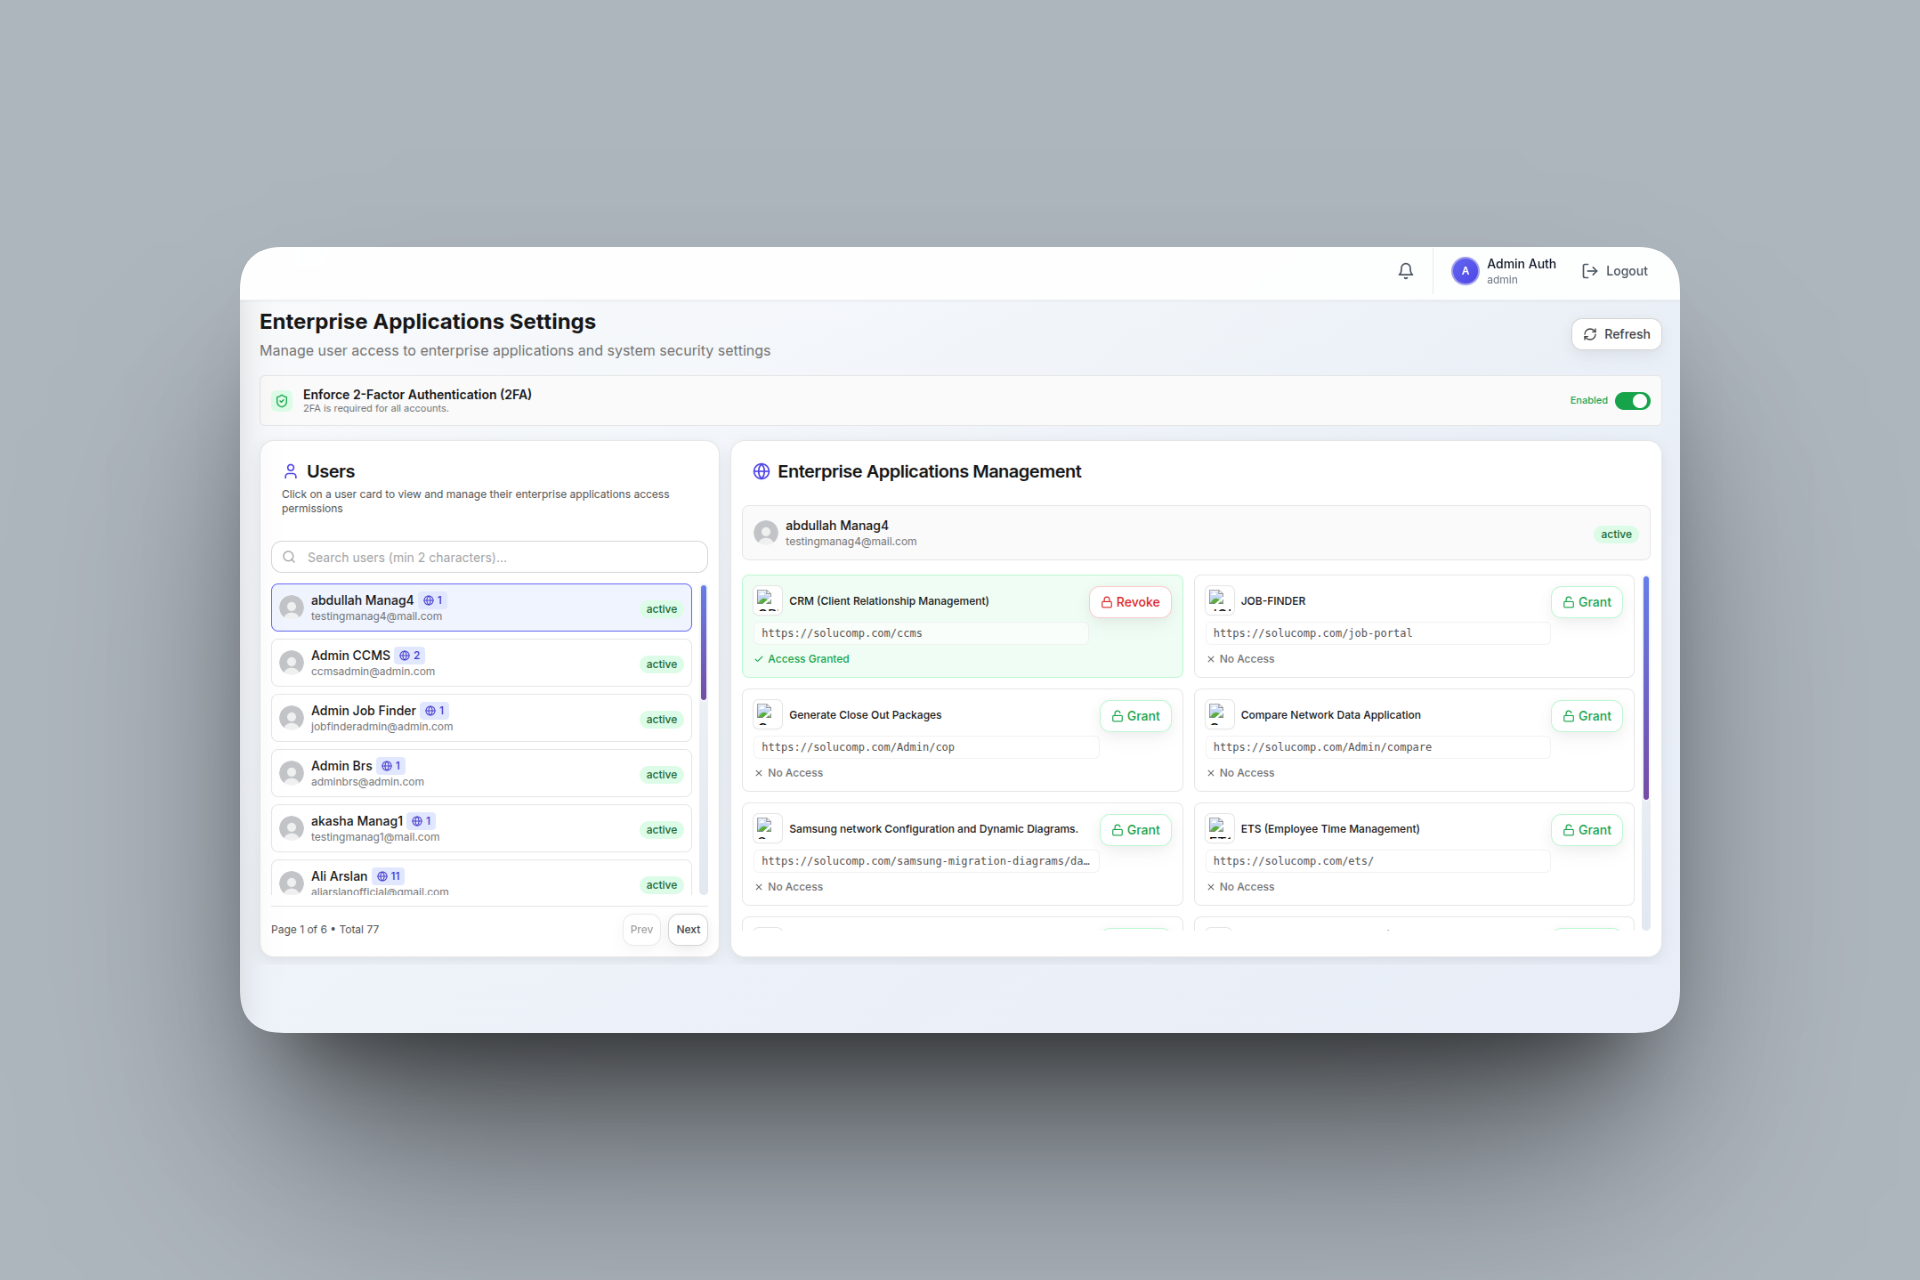
Built React governance portal with real-time access monitoring and user activity charts.
Key System Modules
Centralized Identity Hub
Single-source-of-truth authentication serving independent web applications and services.
Zero-Trust 2FA Security
Google Authenticator TOTP implementation with secure recovery workflows and rate limiting.
Cross-Domain Token Sync
Cryptographically signed JWT sessions with instant revocation and cross-app token validation.
Approval-Based Access
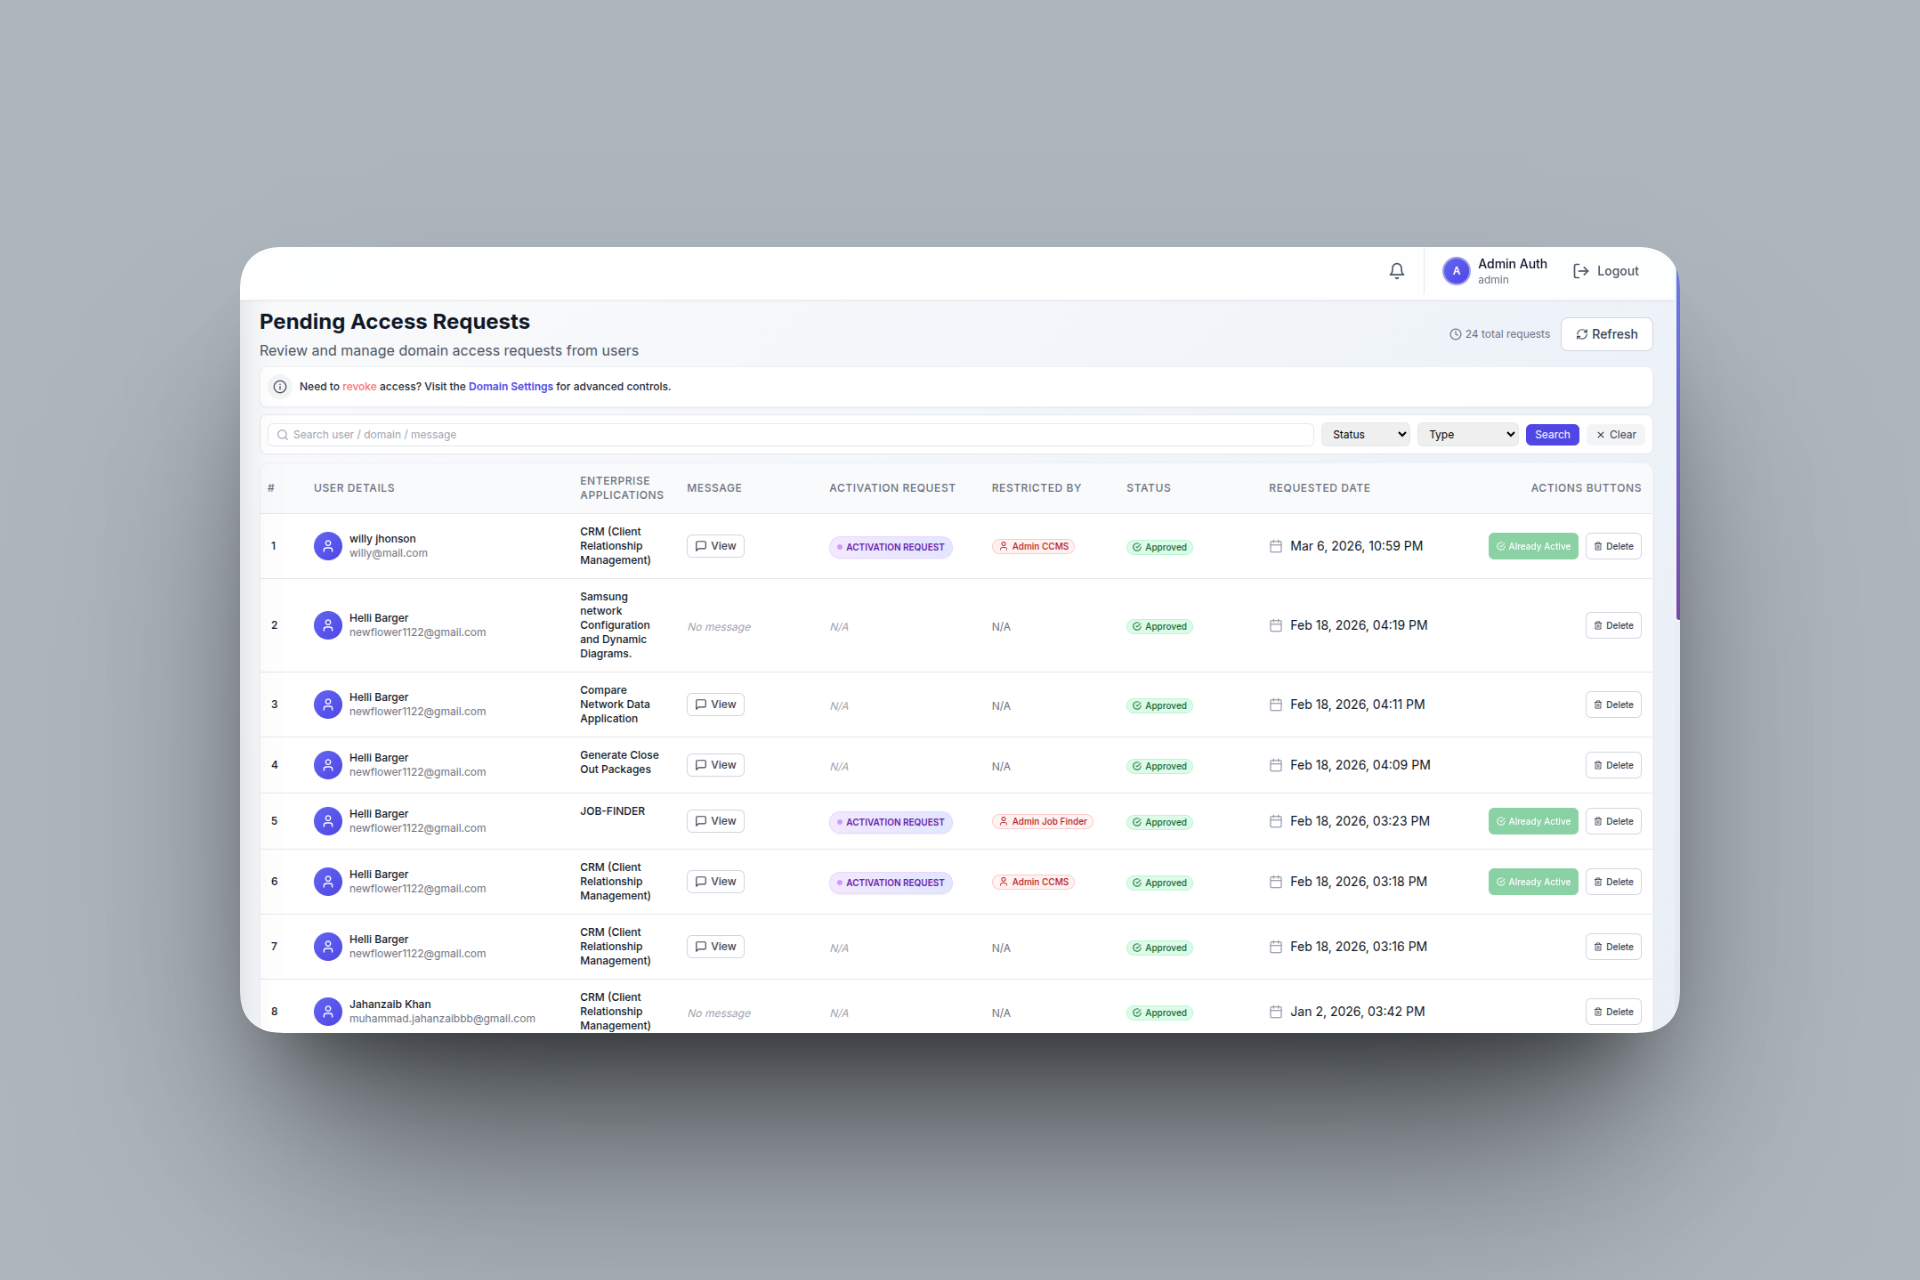
Self-service domain access request pipeline with admin moderation and audit logging.
Bulk Data Processing
Queue-driven Excel ingestion engine processing thousands of site records in the background.
Operational Interfaces
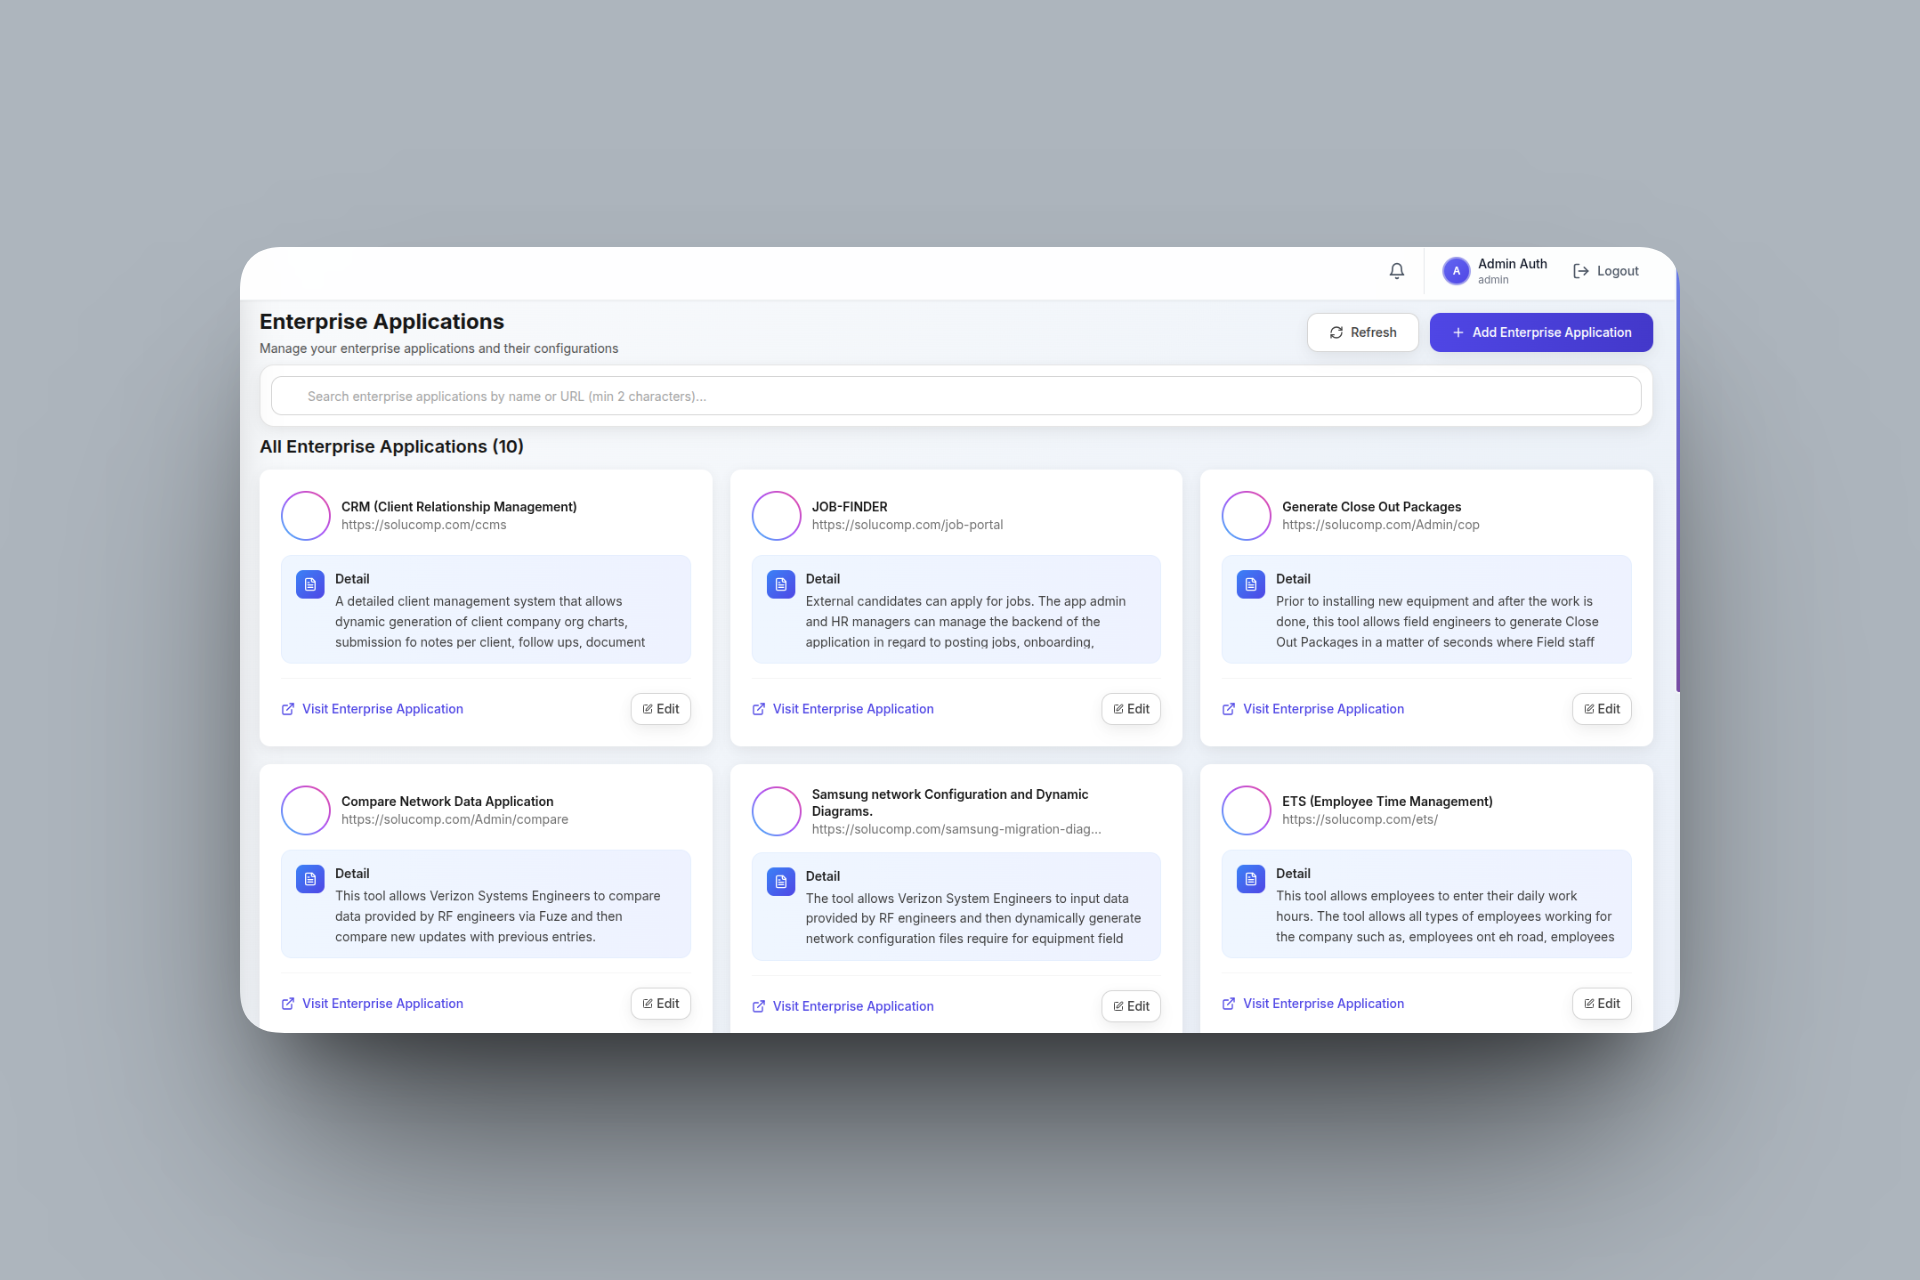
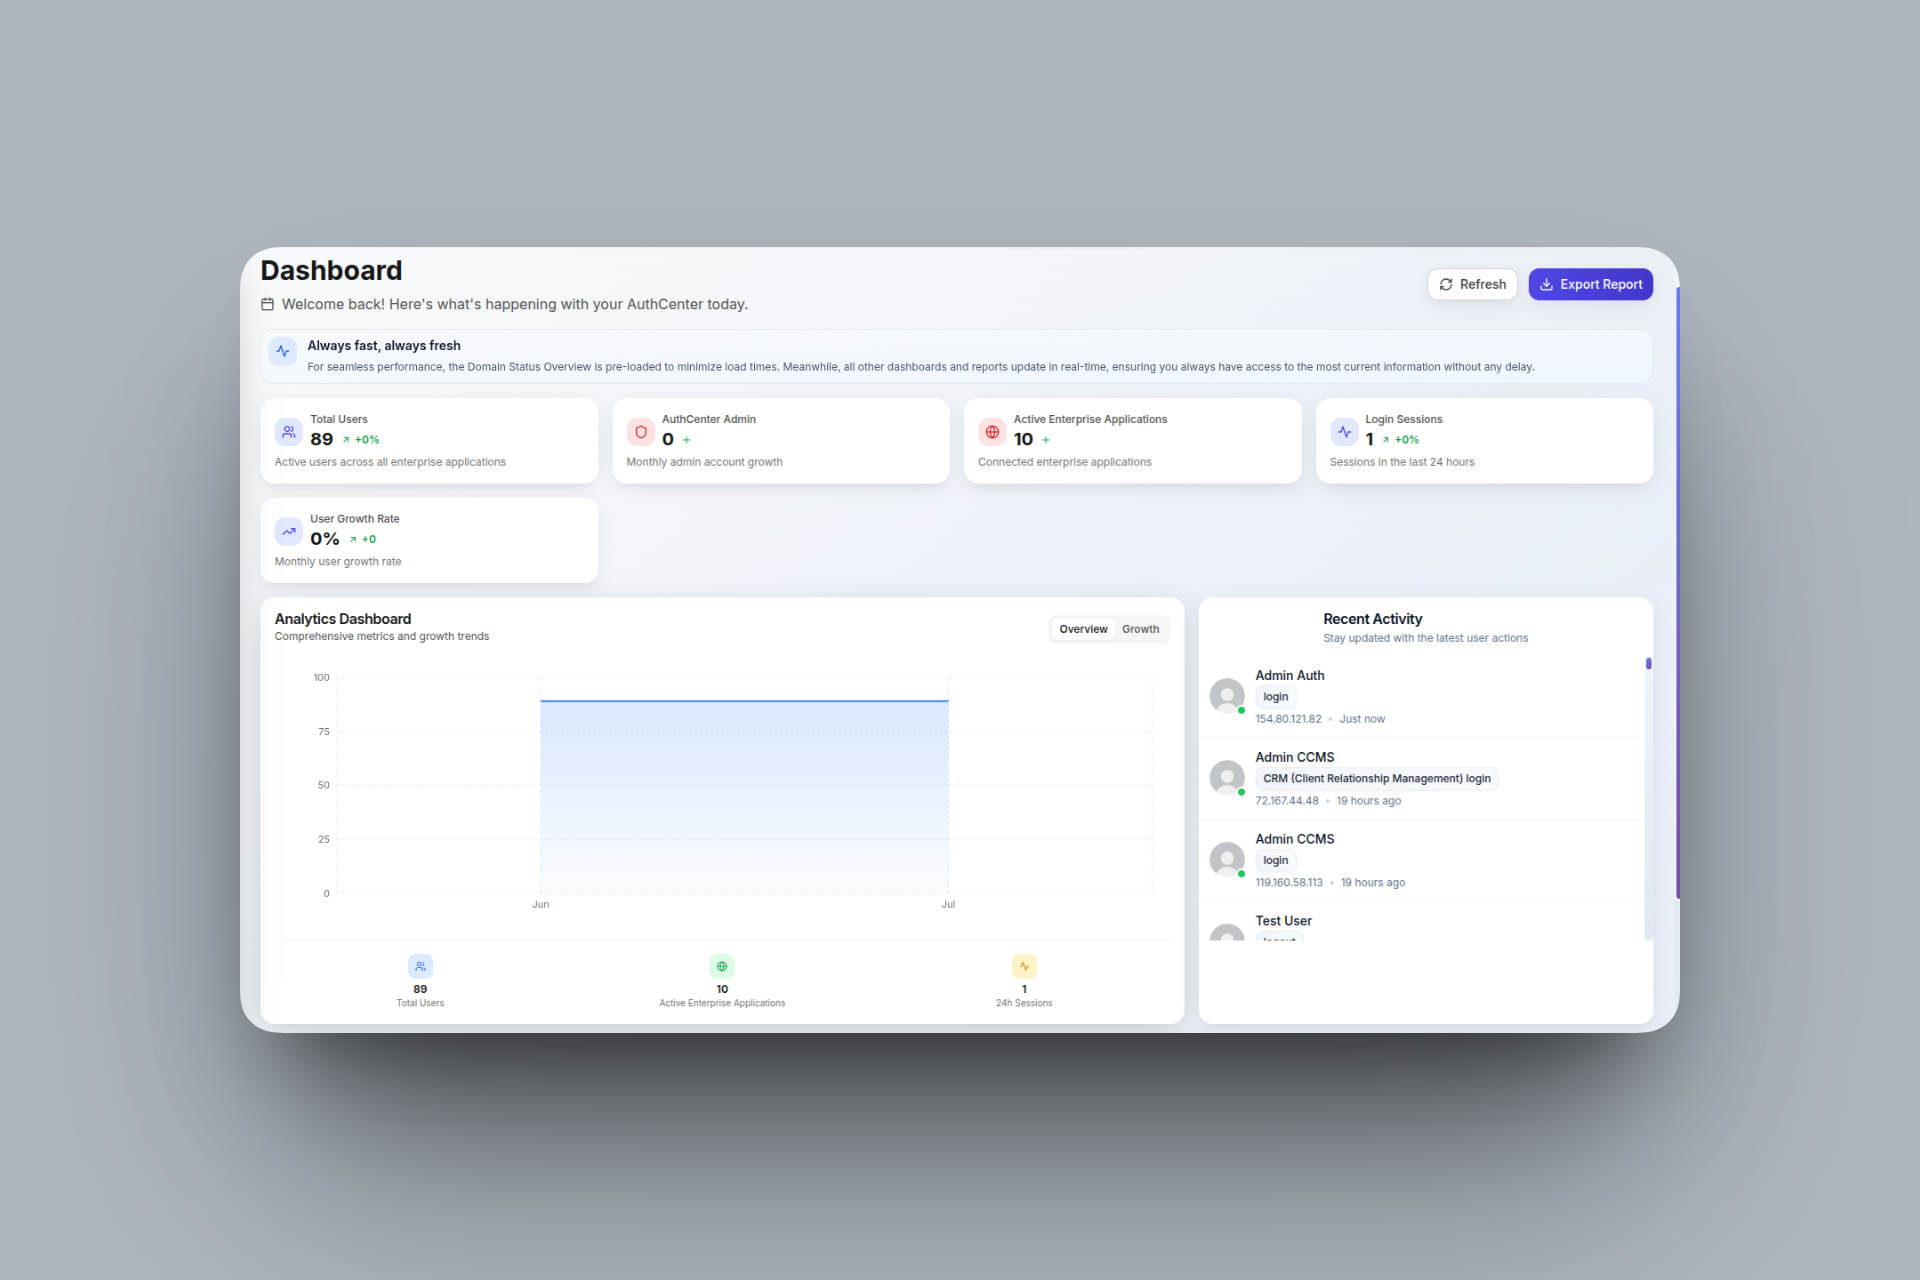
System Topology & Data Flow
Governance Portal & Auth Widgets
React · Vite · Tailwind CSS · Recharts
API & Authorization Layer
Laravel 12 · Token Exchange · Scope Verification
JWT Cryptographic Engine
RS256 asymmetric signing & instant verification
TOTP Multi-Factor Service
Google 2FA enforcement & recovery keys
Background Sync Workers
Asynchronous cross-app provisioning queues
Identity & Session Infrastructure
- •MySQL User & Identity Store
- •Redis Token Blacklist & Session Store
- •Audit Logs & Mutation Ledger
Connected Enterprise Ecosystem
- •CCMS & JobFinder Partner Applications
- •SMTP Security Alerts & Notifications
Technical Deep-Dive & Decisions
Instant Cross-Domain Token Invalidation in Distributed Applications
Stateless JWT tokens cannot be revoked natively until expiry. When an employee is offboarded or a security incident occurs, session access across all connected applications must terminate immediately.
Systematic Resolution
Implemented a hybrid token strategy: short-lived access tokens paired with a centralized Redis token blacklist and webhook event dispatching to invalidate client sessions in real time.
Intentional Design Choice
Adopted standard RS256 asymmetric signing keys so child applications can independently verify tokens while only the central SSO hub holds the private signing key.
Prioritization Rationale
Prioritized instant revocation safety and auditability over pure offline statelessness by introducing a sub-millisecond Redis check on sensitive operations.
Expanded Application Views
Business & Operational Value
Unified corporate authentication into a single secure gateway, eliminating duplicate credentials and reducing employee onboarding friction by 80%.
Achieved zero-trust multi-factor security across all connected enterprise platforms with comprehensive audit logging.
Categorized Stack
LET'S BUILD
YOUR NEXT SYSTEM
Whether you are looking to architect a secure SaaS platform, integrate complex payment gateways, or automate operational workflows, I am ready to help.